Malware Analysis From Fundamentals to Threat Intelligence
Every security team eventually meets a file it doesn’t understand. Malware Analysis: From Fundamentals to Threat Intelligence teaches you how to find out what that file does, how to stop it, and how to turn what you learn into defenses your organization can use.
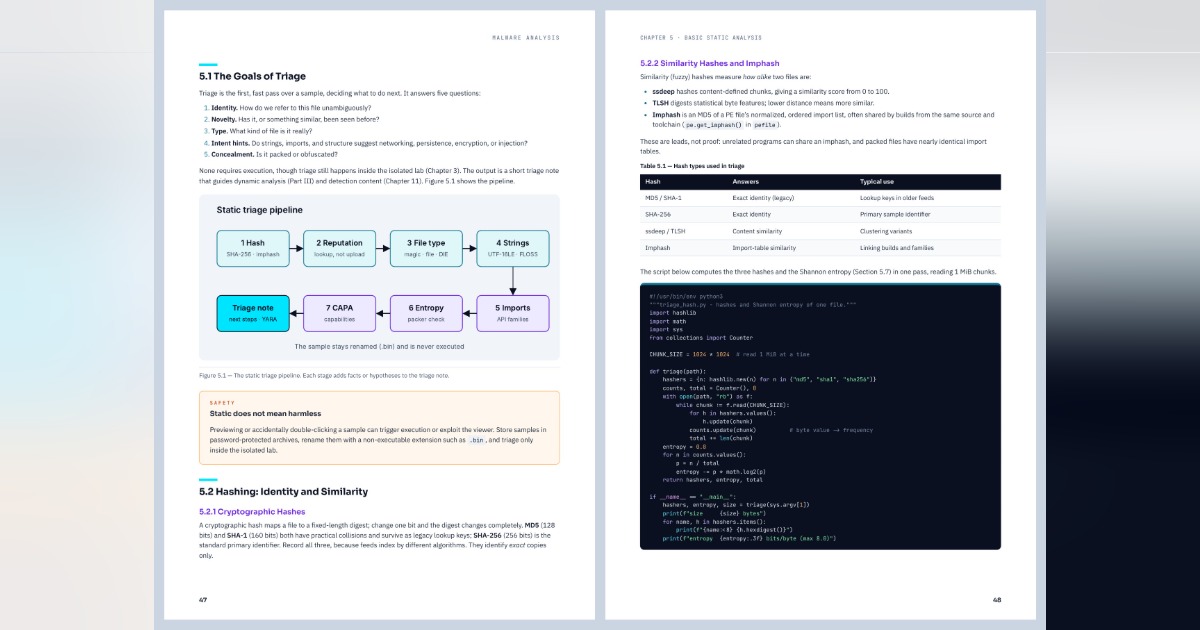
This practical guide takes you from first principles to professional practice. You will build a safe, isolated analysis lab and learn to read executable file formats. You will triage samples with hashes, strings and entropy, and navigate code in Ghidra. You will watch malware behave in a sandbox and uncover hidden code in memory with Volatility 3. Then you’ll learn the step most books skip: turning findings into YARA and Sigma detections, MITRE ATT&CK mappings and intelligence reports.
One fictional sample runs through every chapter, so you follow a single investigation from first triage to final report. Case studies of WannaCry, NotPetya and Emotet show how real-world analysis shaped real-world response.
Each chapter includes learning objectives, safe lab exercises, worked examples, common mistakes, a summary, and review questions with answers. Written for cybersecurity students, SOC analysts, junior malware researchers and incident responders, it focuses on authorized, defensive work.